The companies putting AI agents to work are securing them with 1Password
상시 권한은 가장 큰 보안 위험 요소입니다
상시 액세스의 96% 이상이 사용되지 않은 채 남아 있습니다of standing access sits unused
권한은 처음 부여된 작업이 끝난 뒤에도 그대로 남아 있습니다.
출처: Gartner, Innovation Insight for Cloud Infrastructure Entitlement Management88%의 침해 사고는 기존 액세스 권한을 악용해 발생합니다of breaches exploit existing access
공격자는 정리되지 않고 남아 있는 역할을 사용합니다.
출처: Verizon DBIR 2025From standing access to zero standing privileges
01. Request access where work happens
Users request access from Slack, Teams, the CLI, or ServiceNow, for themselves or their agents. Every request is tied to an intended action instead of relying on invisible standing privilege.
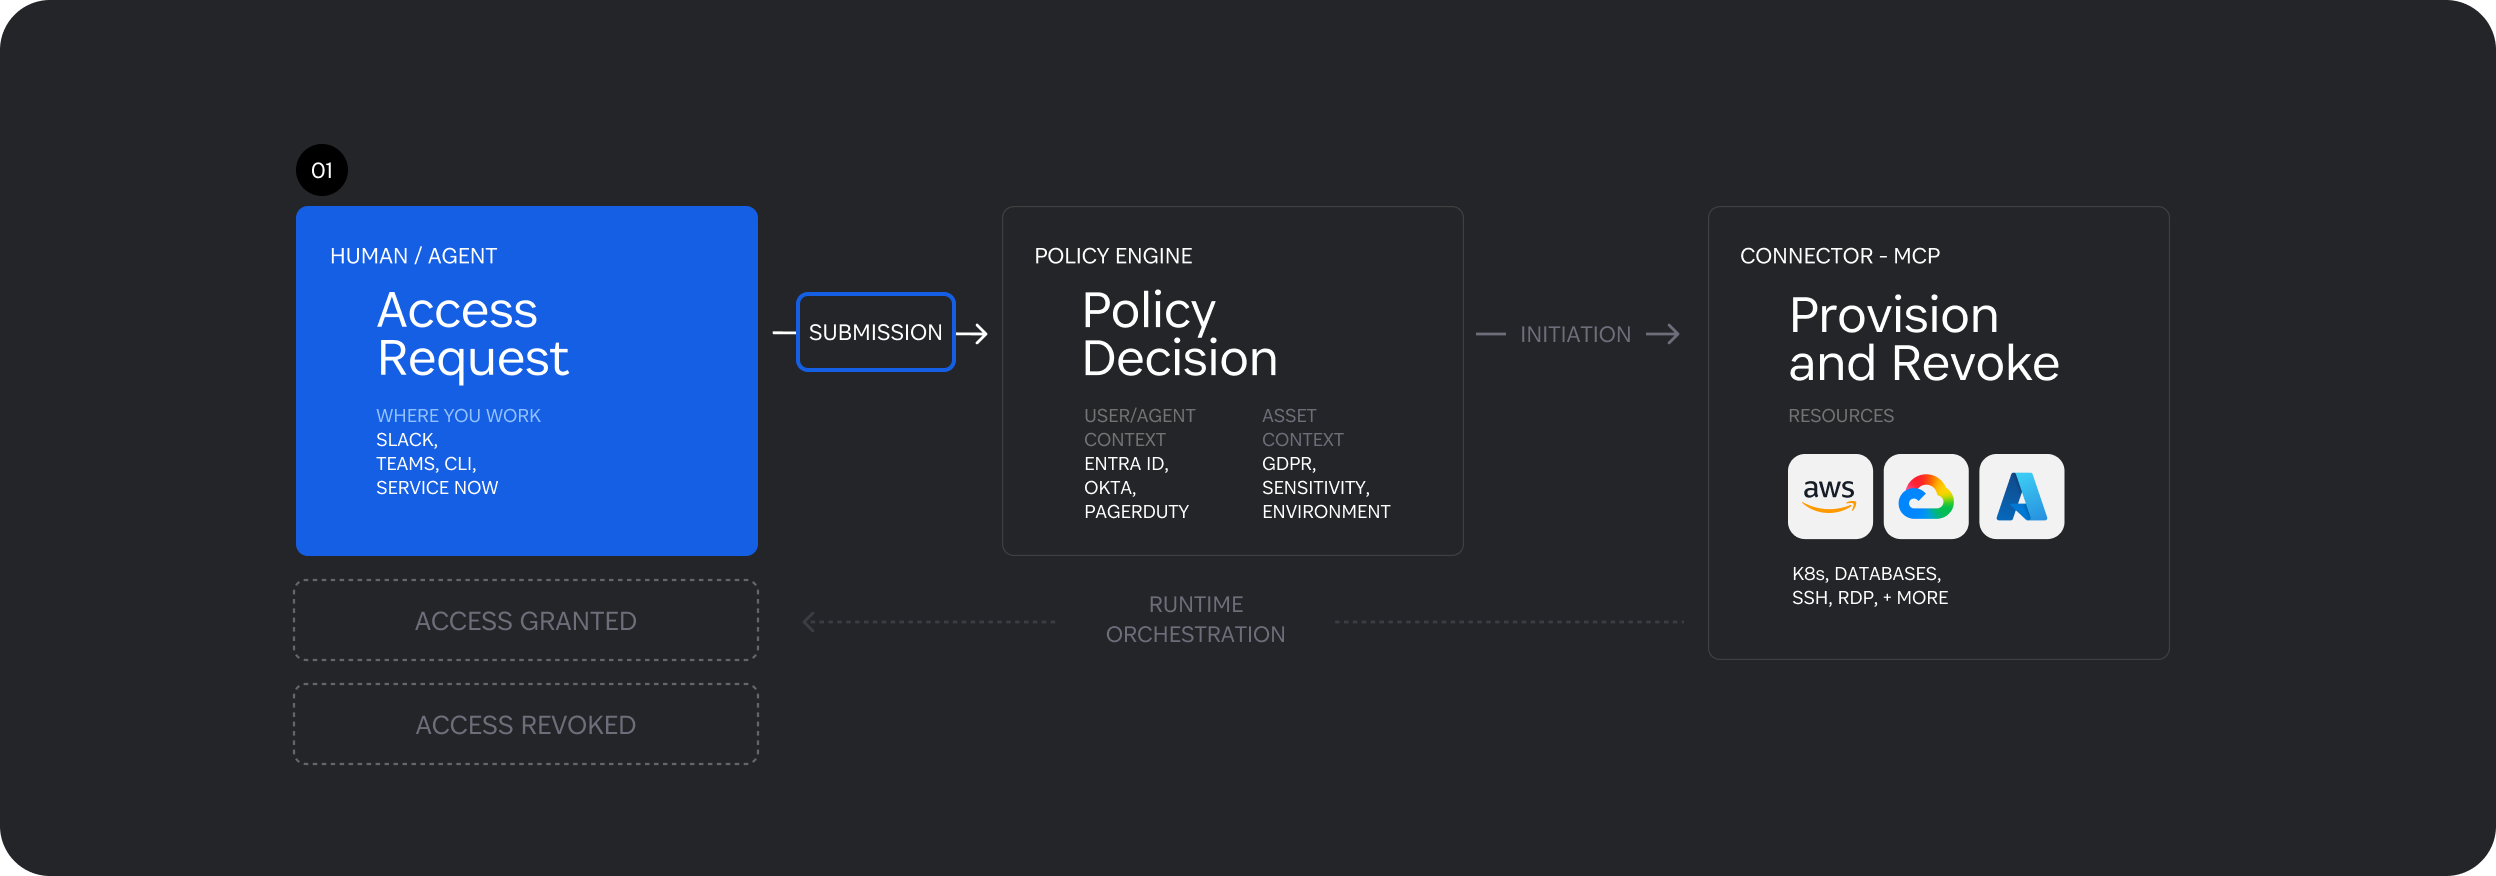
02. Evaluate every request in context
Policy decisions draw from Entra, Okta, PagerDuty, asset context, and sensitivity. Every request is evaluated at the moment it arrives, automatically or with a human in the loop depending on your approach.
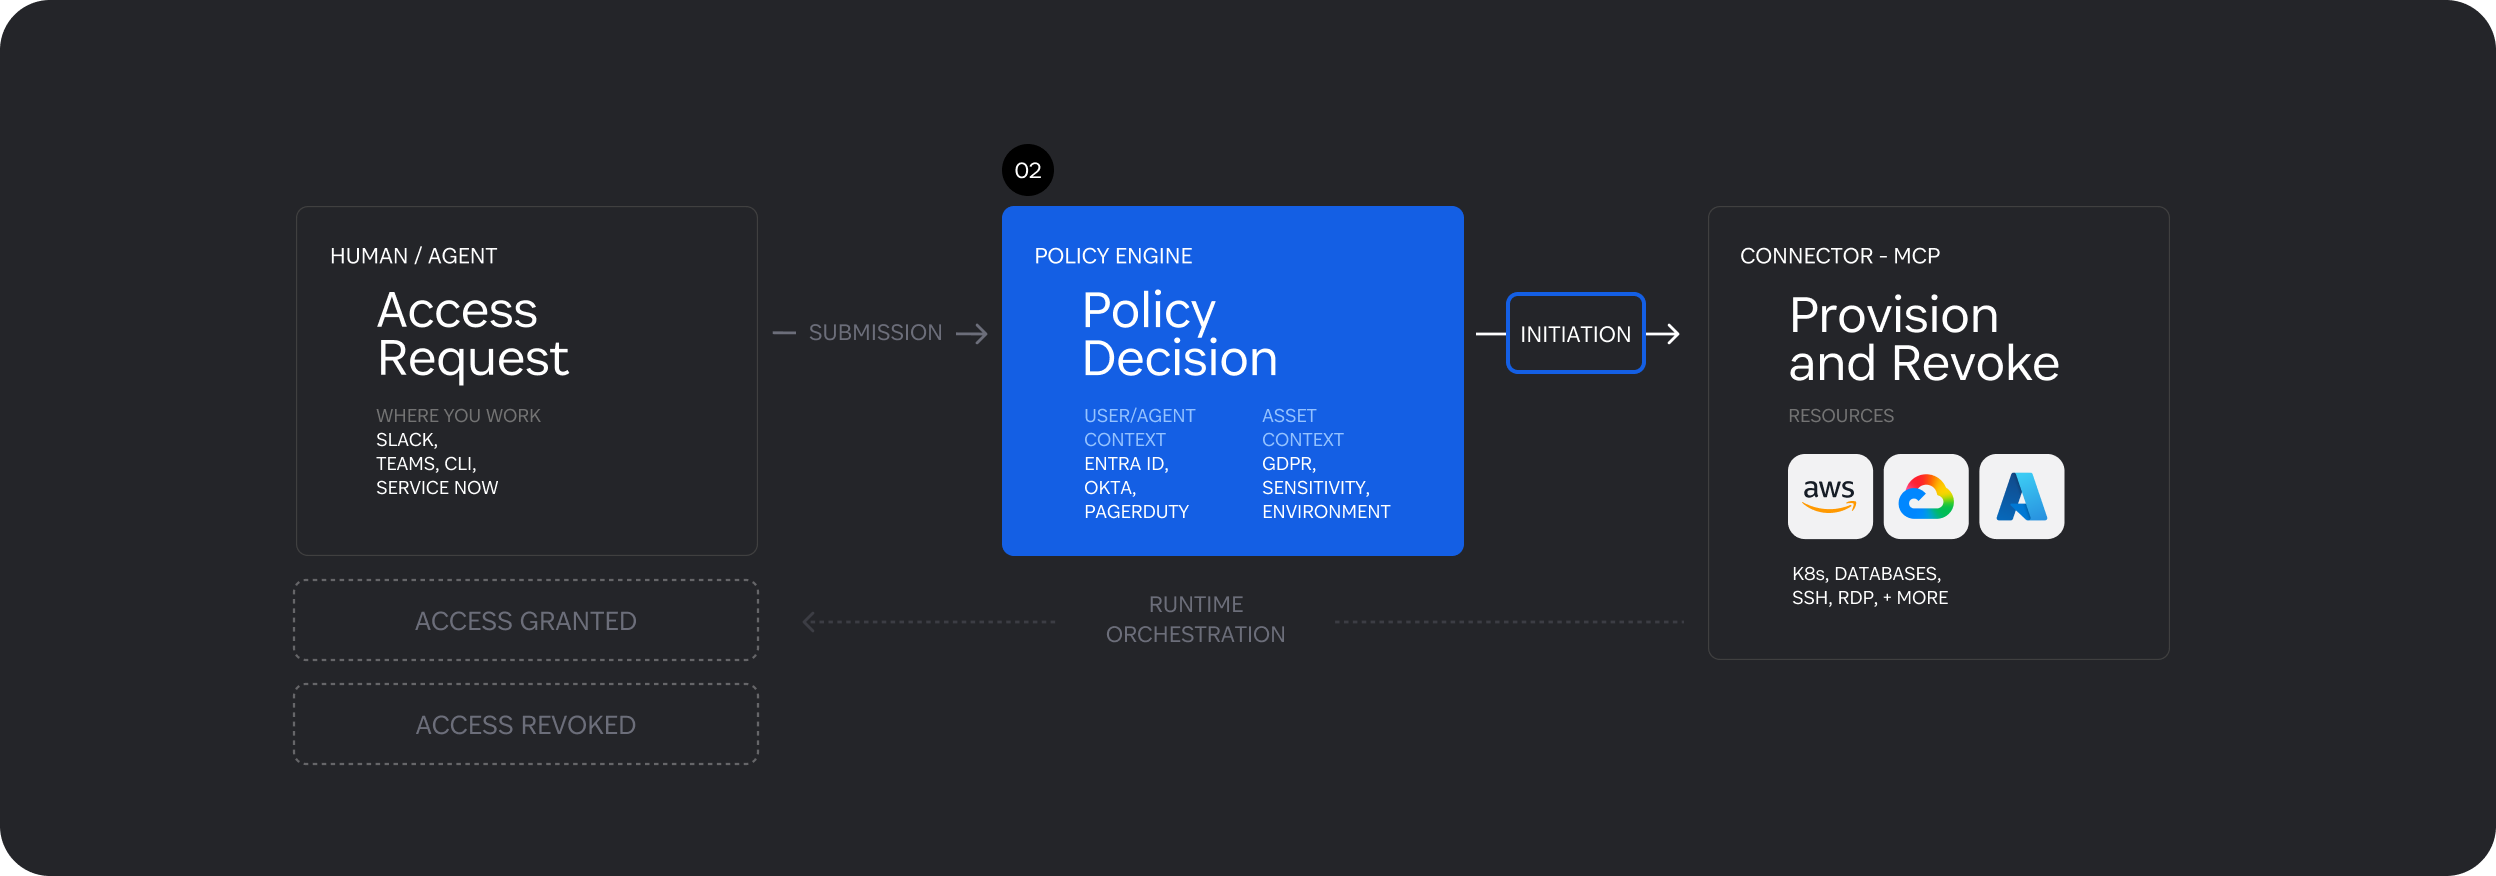
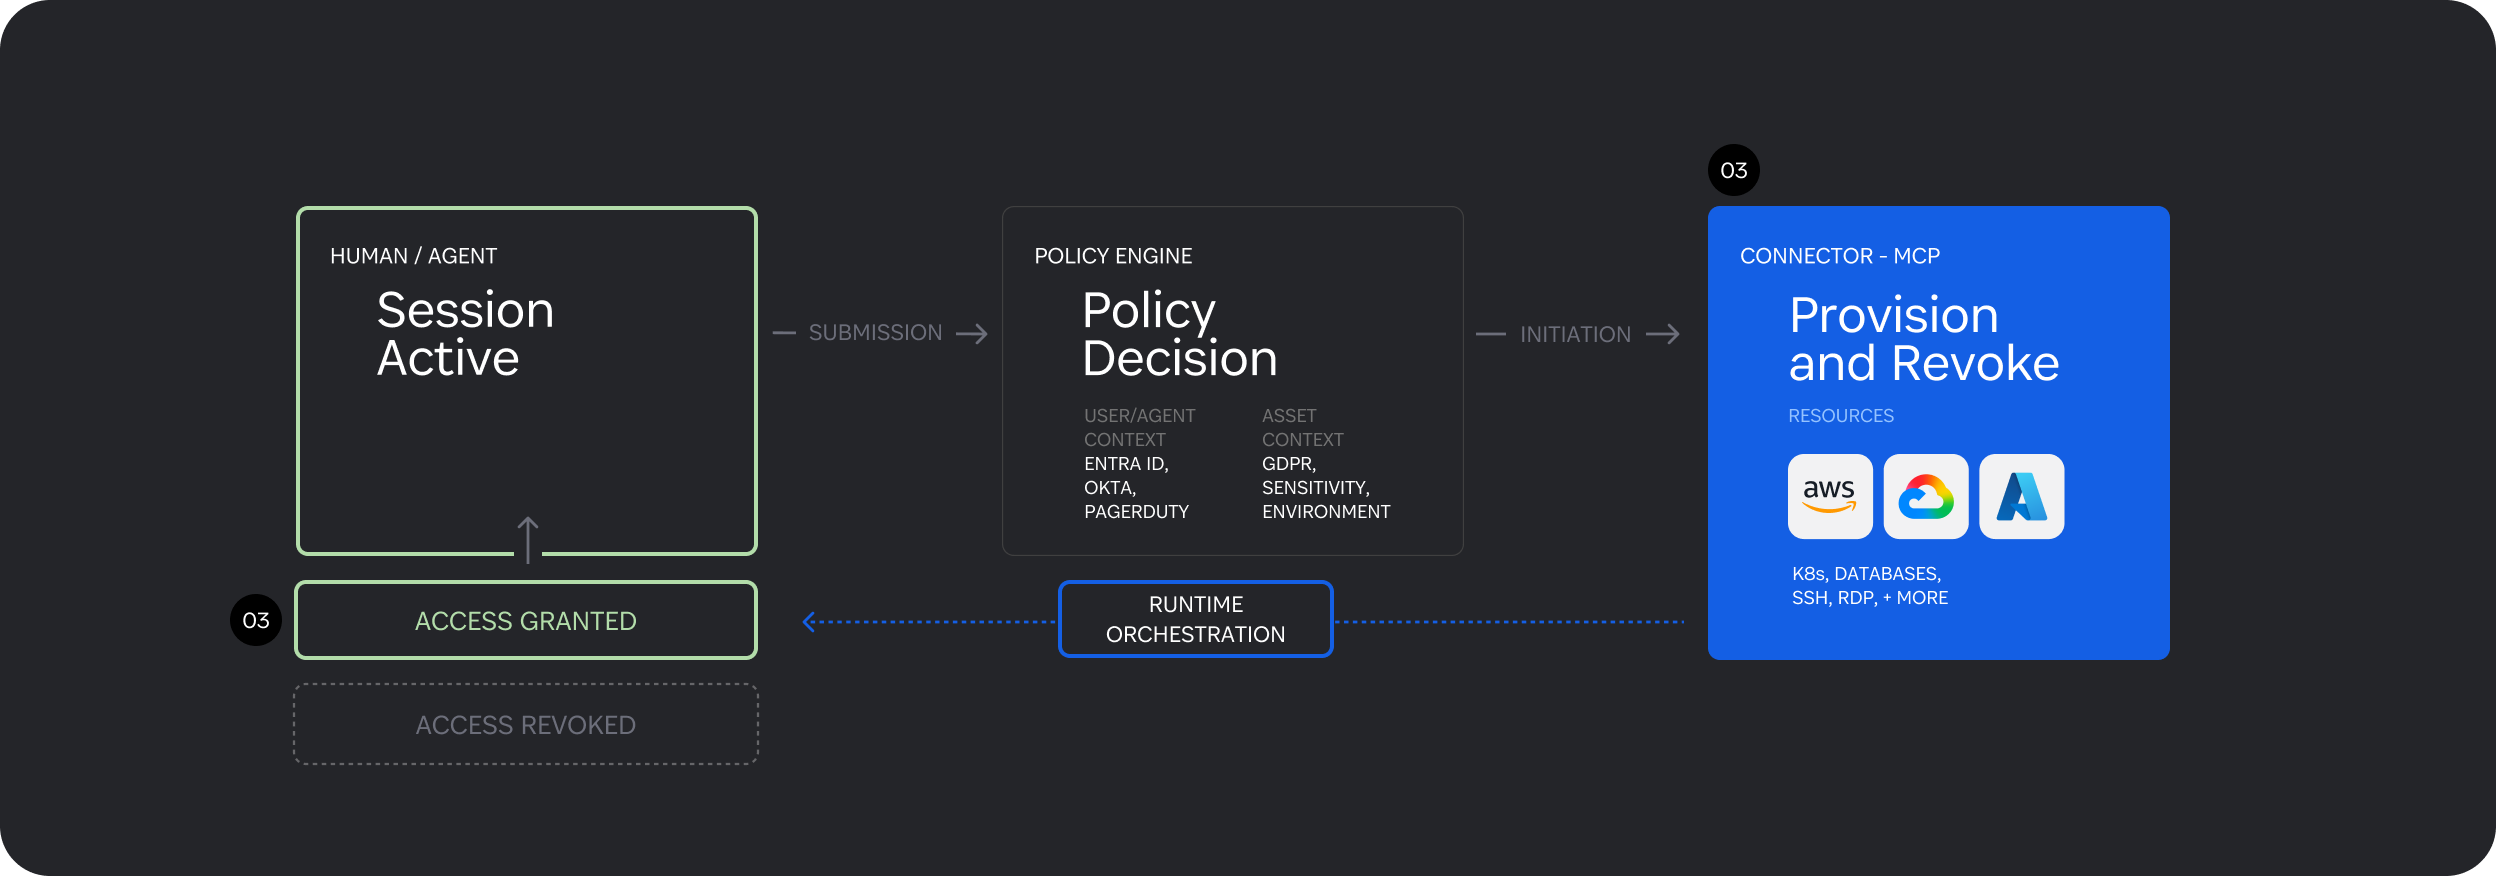
03. Provision minimum access, just in time
A lightweight connector in your environment provisions just-in-time, just-enough access to Cloud Infra, K8s, databases, SSH, RDP, and more. Agents connect via MCP. Everything is scoped to need and policy.
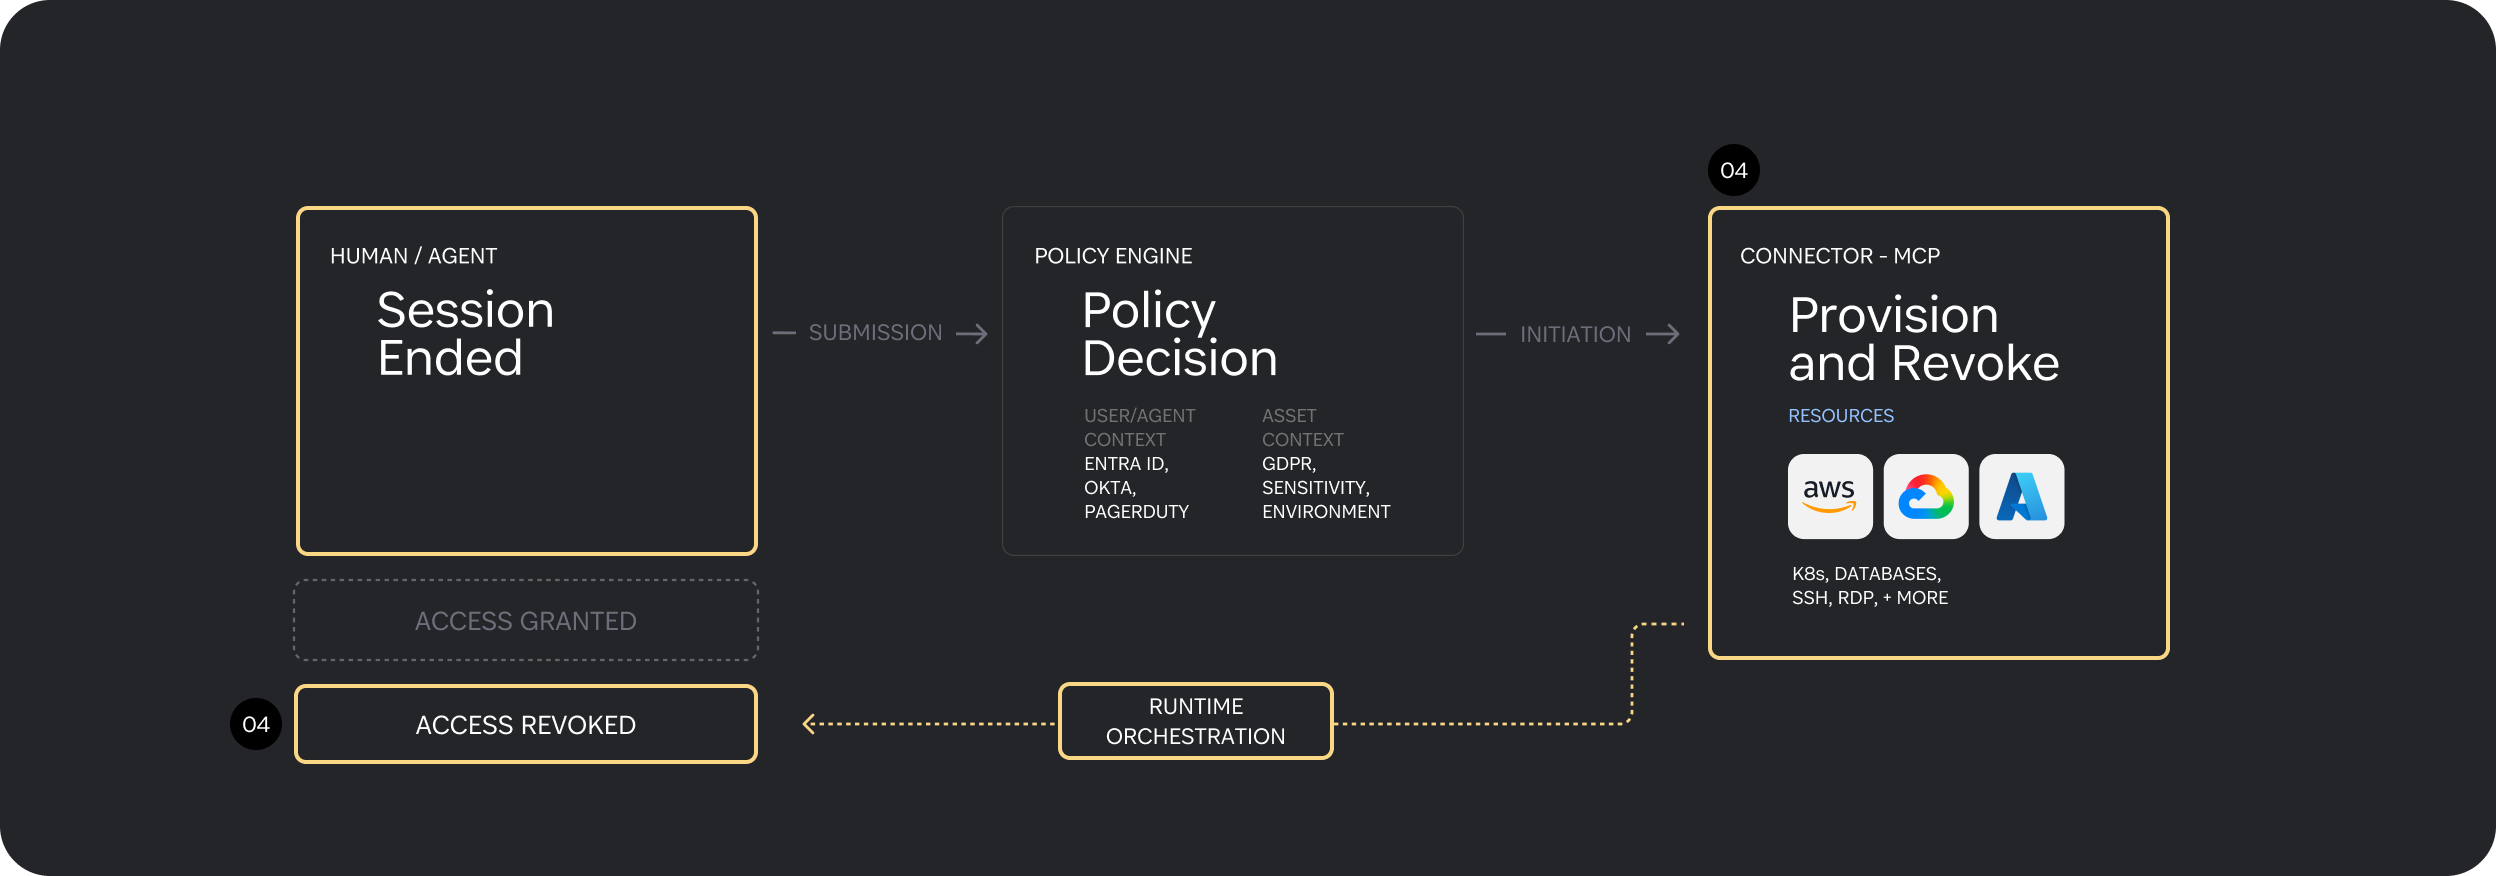
04. Every decision leaves a trail
When a session ends or risk changes, access is revoked. Every request, decision, and revocation is captured with context and surfaced through the audit log and SIEM integration, so teams can see what happened and why.
AI 에이전트 제어
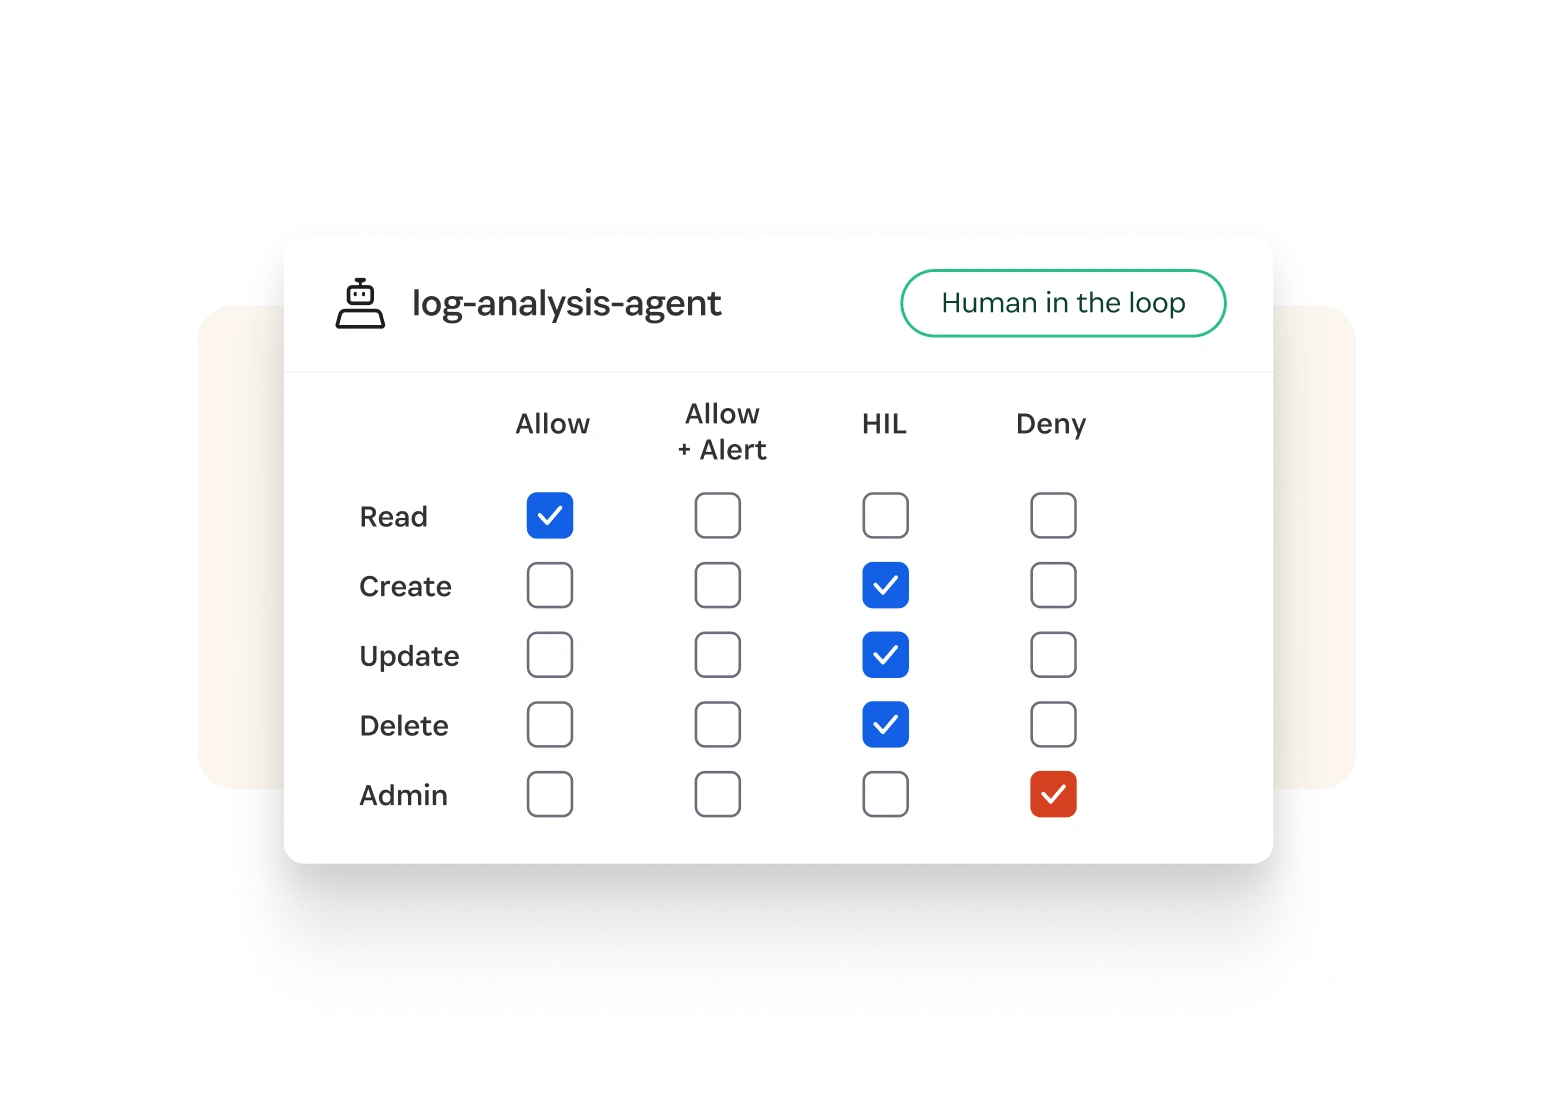
- 상시 액세스가 없는 작업 전용 아이덴티티
- 의도 기반 액세스 제어(IBAC)를 통한 실시간 모니터링
- 모든 에이전틱 워크플로에서 영향 범위 축소
적시 액세스
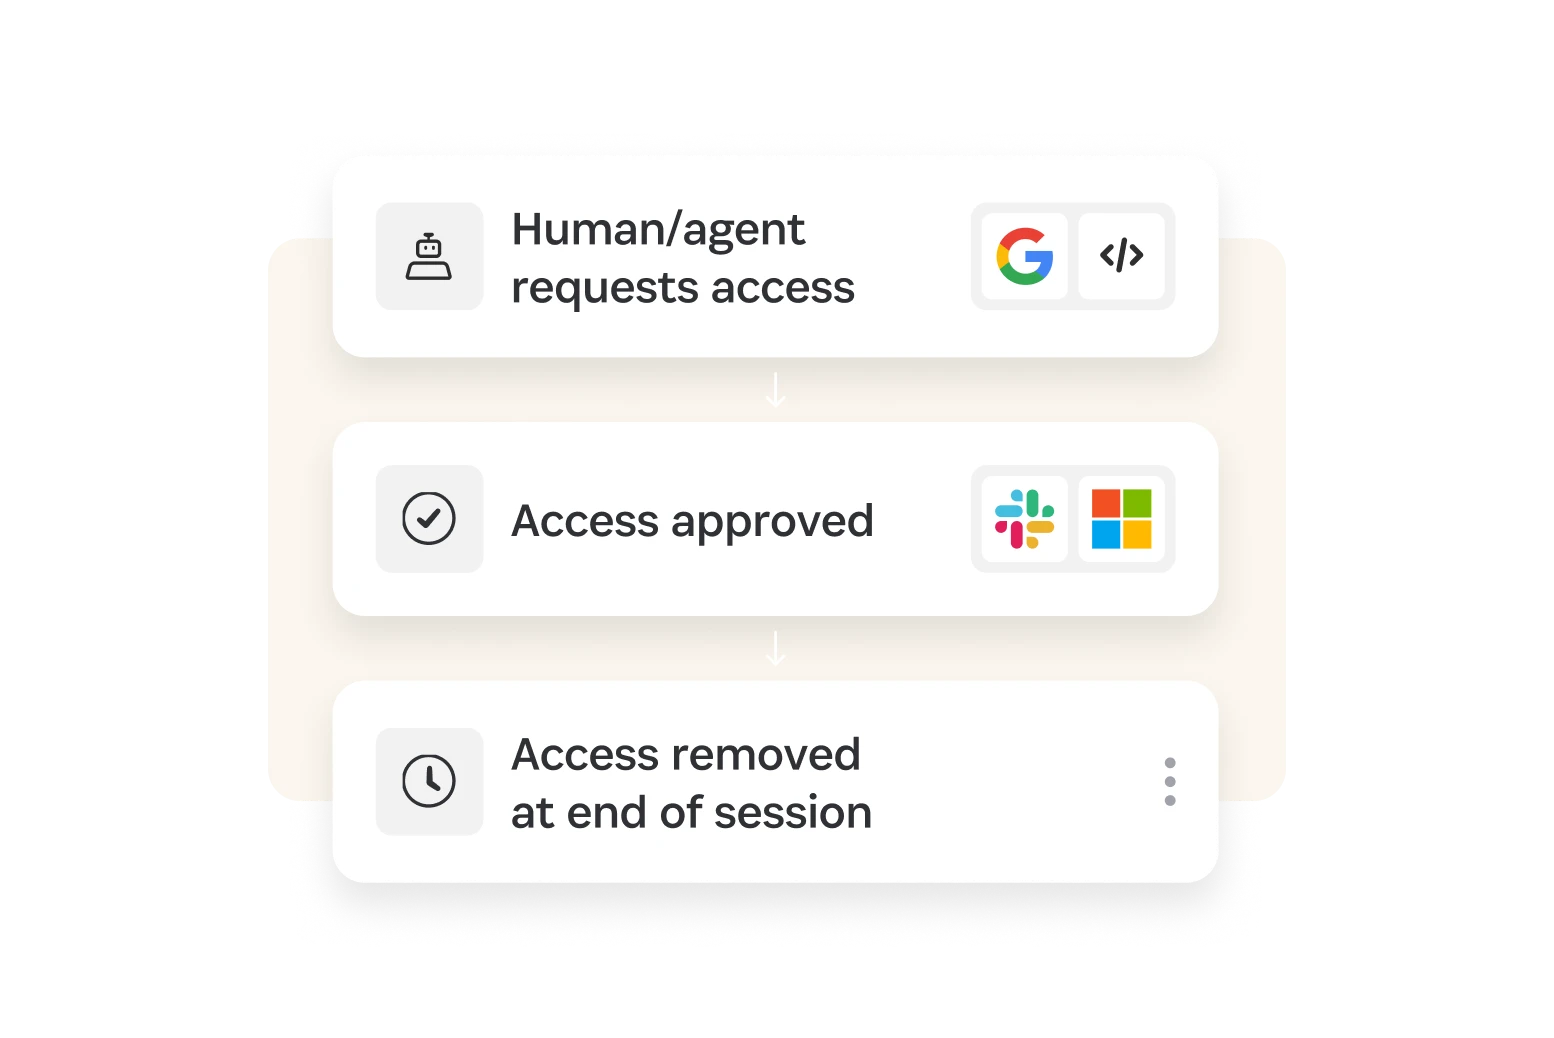
- 환경 전반에서 정밀하게 범위가 지정된 권한
- Slack 팀, CLI 또는 MCP에서 액세스 권한 요청, ITSM 도구와 통합
- 저위험 요청에 대한 정책 기반 자동 승인
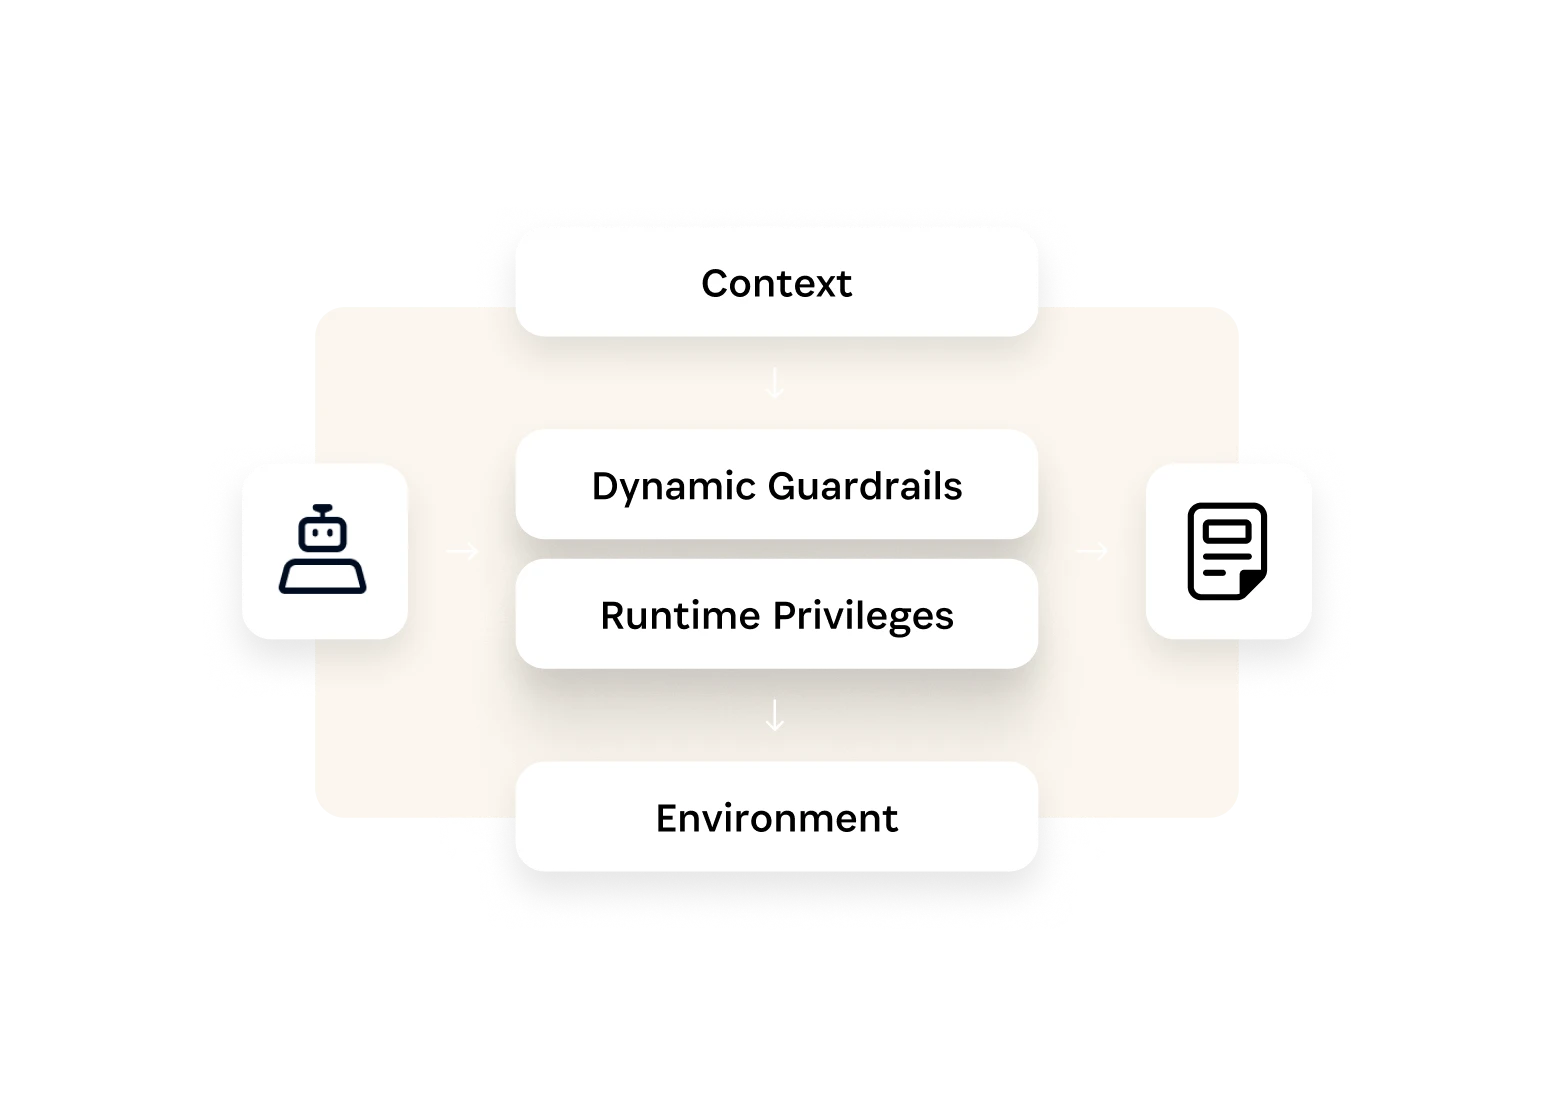
동적 가드레일
- 모든 액세스 결정에 비즈니스 컨텍스트 반영
- 클라우드, K8s, 데이터베이스 전반에 걸친 위험 기반 정책 적용
- 정책은 환경이 성장함에 따라 쉽게 수정하거나 보강할 수 있어요
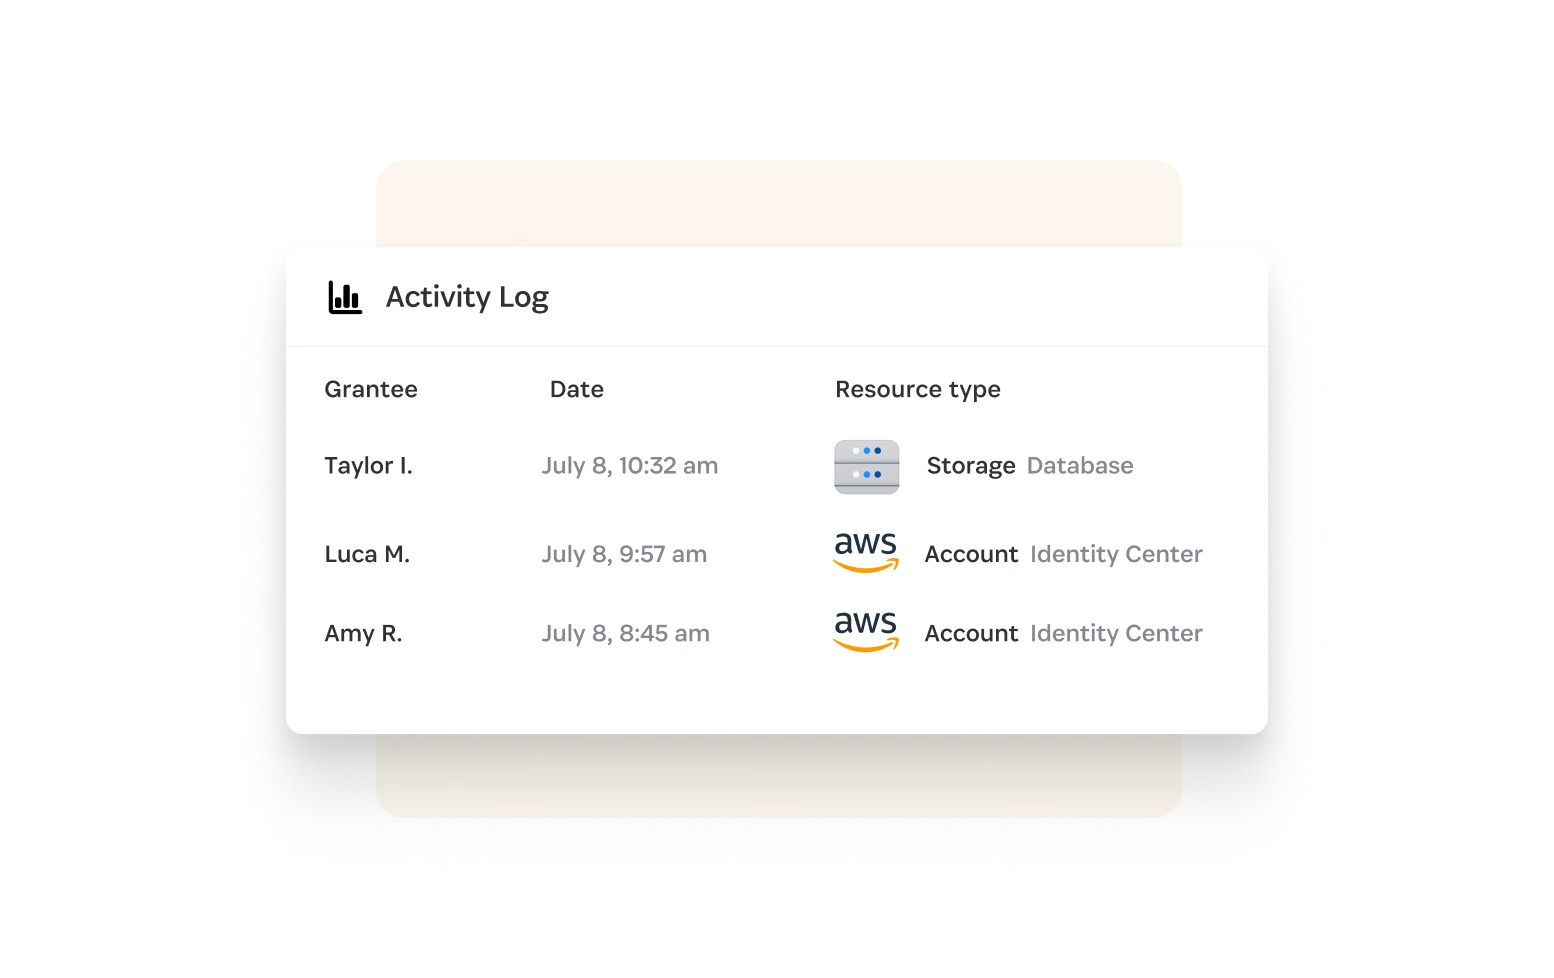
감사 및 규정 준수
- 규정 준수 보고
- 비정상 패턴에 대한 자동 이상 탐지
- 모든 액세스 이벤트에 대한 전체 비즈니스 컨텍스트
1Password recognized in the 2026 Gartner® Magic Quadrant™ for Privileged Access Management
1Password Privileged Access was named an Honorable Mention.
Privileged Access는 Unified Access 플랫폼의 일부입니다
모든 ID의 액세스를 파악하고 보호하며 감사하는 플랫폼입니다.
Privileged Access FAQ
적시 권한 액세스란 무엇인가요?
적시 액세스란 적합한 ID에 올바른 액세스 권한을, 꼭 필요한 순간에만 제공하는 것을 의미합니다. 적시 액세스는 요청 시 생성되고, 특정 작업에 맞게 범위가 지정되며, 세션이 종료되면 제거됩니다.
1Password Privileged Access는 어떤 기능을 하나요?
1Password Privileged Access는 상시 권한을 어떻게 제거하나요?
1Password Privileged Access는 AI 에이전트를 어떻게 보호하나요?
1Password Privileged Access에는 프록시나 배스천 호스트, 서버별 에이전트가 필요한가요?
1Password Privileged Access는 1Password® Unified Access 플랫폼에 어떻게 통합되나요?
1Password Privileged Access는 감사 및 규정 준수를 어떻게 지원하나요?
상시 액세스 제거
클라우드, 데이터베이스, K8s 환경 전반에서 적시 액세스가 어떻게 프로비저닝되고 제거되는지 확인해 보세요.